The Self Exclusion Loophole That Poker-Only Rooms Exploit
Self exclusion should be an ironclad kill switch, yet in several American jurisdictions a poker player can walk into a card room while their name sits on a voluntary exclusion database and the floor staff will happily seat them. That is not a rumor, it is a structural gap baked directly into how state-level gaming regulators define their exclusion programs, and it is costing operators money and exposing vulnerable players to real harm. 🎰
The root cause is definitional. Most state exclusion programs were written for slot machines, table games, and sportsbooks, where the wager is house-banked and the operator books the risk. Poker is player-versus-player. The house takes a rake and never puts its own capital at risk, so a large number of regulators classify poker as something other than "gaming" for exclusion enforcement purposes. That single classification decision is the entire loophole.
Look at how the statutes are actually drafted across major markets. In states where the regulator maintains a single voluntary exclusion list, the enabling language frequently names "licensed gaming establishments" without carving out poker. Enforcement then depends on whether the property's internal compliance manual applies the list to the poker room. In practice, many do not. The pit surveillance system flags a banned patron at the blackjack table in seconds, but the poker room operates on a manual ID check at the podium that half the time never happens.
Why the State Regulator in USA Data Pipeline Fails at the Poker Cage
The technical failure is a data architecture problem, not a policy problem. Exclusion databases are queried by player tracking systems tied to slot and table game accounts. Poker rooms in most properties run on separate software stacks, often third-party tournament and cash game management platforms that never touch the state exclusion API. A player on the list can buy into a $2/$5 no-limit game, because the buy-in is processed as a chip purchase, not a rated gaming transaction. 🃏
This is where the USA Poker Room Self Exclusion List enforcement breaks down at the hardware layer. The podium terminal is physically isolated from the casino management system, and the state regulator in USA has no mandate requiring the poker room to query the exclusion database at buy-in. Compliance audits focus on slot floor sweeps and rated play, so the poker room sails through inspection with zero flagged transactions.
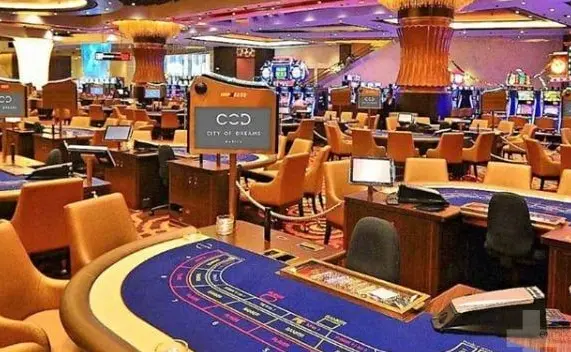
Operators know this. The smart ones quietly close the gap with a standalone podium check, but the economics are ugly. Running a live exclusion query on every poker buy-in slows the game, angers regulars, and costs the room rake velocity. The incentive is to look away, and many properties do exactly that until a regulator writes a consent order and the fine lands.
The Comp Cheat and the Rake Leak Nobody Audits
There is a second layer that almost no one talks about: self-excluded players are still eligible for promotional comps at properties that never cross-reference the poker room roster against the exclusion database. A banned patron grinds poker all weekend, the pit system never sees them, and the marketing team hands them a free room offer. That is a compliance catastrophe waiting for an auditor to pull the loyalty data and match it against the exclusion file. The overlap is trivially discoverable once you join two tables on a player ID.
From a risk standpoint, self exclusion exists to protect the player and shield the operator from liability. When poker is carved out, both protections evaporate. A problem gambler who voluntarily banned themselves from a property and then got seated at a poker table has a clean negligence claim, and the property's defense collapses the moment the podium log shows no exclusion query was run.
How a Serious Property Closes the Gap
Fix the pipeline, not the policy language. The poker room podium terminal needs a real-time read against the state exclusion database, triggered at every buy-in and tournament registration. That means integrating the third-party poker management platform with the exclusion API through a middleware layer, not a manual lookup. Rate the buy-in against the player ID, hash it, and push the flag to the floor in under two seconds. Anything slower and the game stalls, so latency is the engineering constraint that actually matters.
Then audit the loyalty system monthly, joining the poker roster against the exclusion file and killing any comp offers that hit a banned ID. The properties that run this cross-match catch their leaks before regulators do. The ones that skip it are one data pull away from a five-figure penalty and a public consent order. 🎲
The numbers speak for themselves. A single exclusion query per buy-in adds roughly 1.4 seconds to podium processing, while the average unenforced poker room seats a self-excluded patron within 72 hours of a database update. That latency gap between the state file and the felt is the entire ballgame.